Sudo yum install iptables-services. History of nftables in RHEL CentOS.
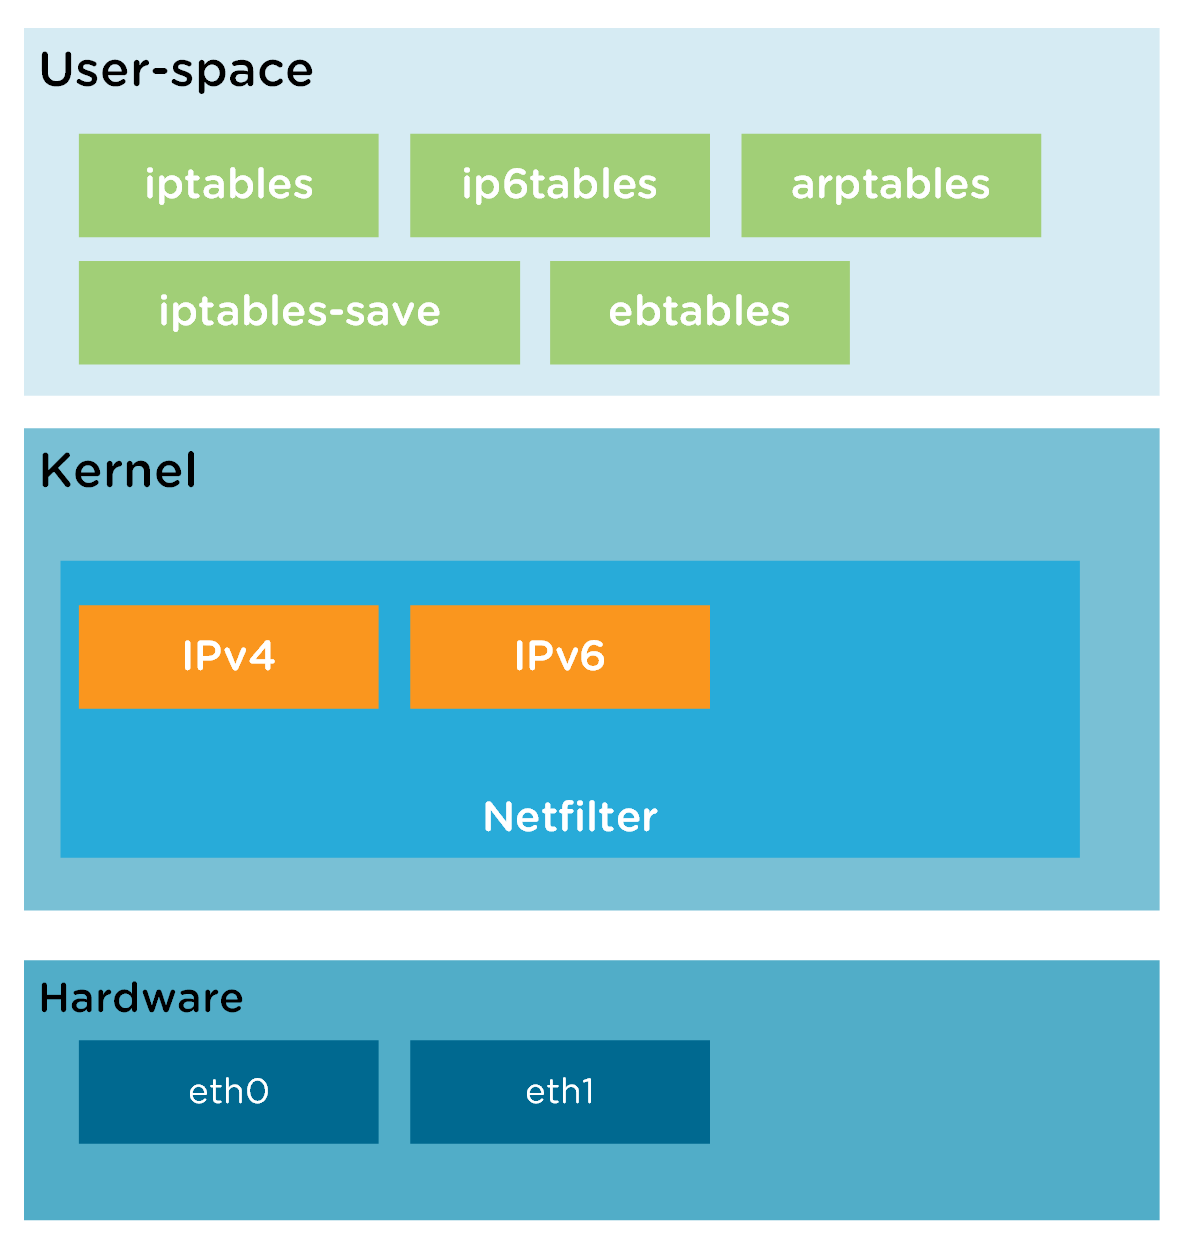
Essential Linux Skills With Centos 7 Secure Firewall With Iptables
While it is decentralized and has one of the most diverse NFT collection the service still has its limitations.
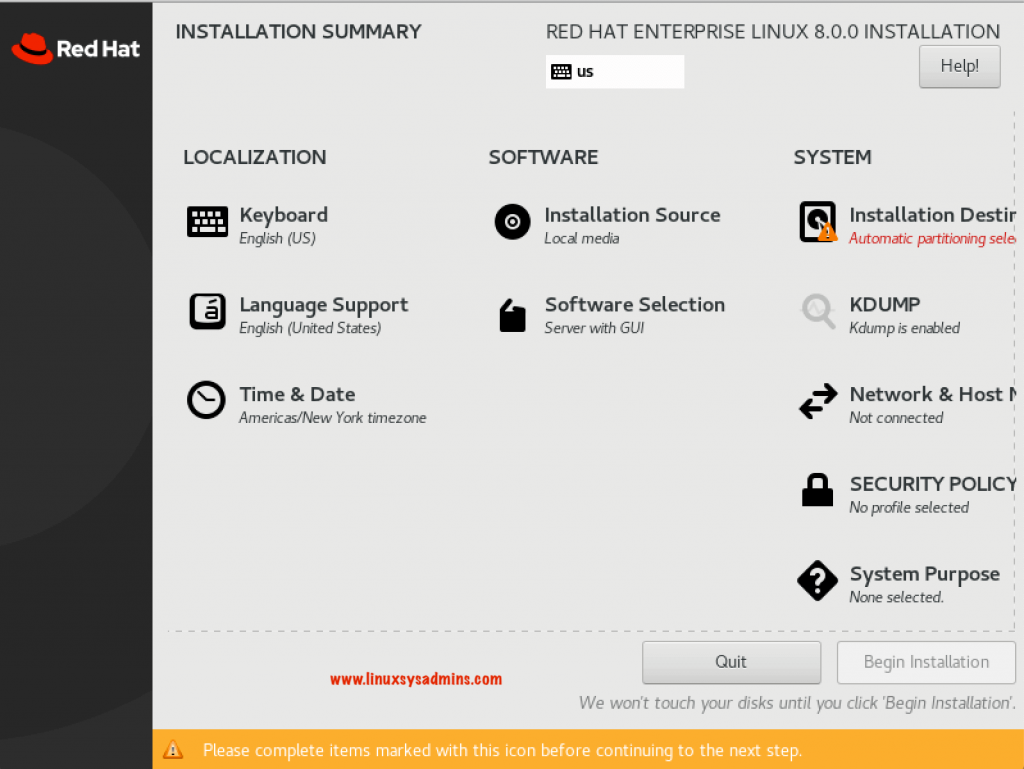
Rhel 7 nftables. 1 root root 17 Mar 17 1022 usrsbiniptables - xtables-nft-multi. These samples often include the setup of. Nftables를 사용하여 포트 전달 구성.
Using nftables in CentOS 8 is the lesson we look at todayThe default backend firewall module used by the Linux kernel 418 in Red Hat Enterprise Linux 8 and CentOS 8 is nftables. If you specify only a file name without an absolute or relative path nftables includes files from the default search path which is set to etc on Red Hat Enterprise Linux. For that reason the nftables syntax is shorter and easier to understand.
Next disable and stop the firewalld service. One of the most prominent and one that comes pre-installed and as a default firewall management tool is firewalld. Creating a rule with a counter.
You can exchange your fiat currency using a credit card or Paypal via these reputable websites to exchange it for crypto. Fedora 18 and newer. Using nftables to limit the amount of connections.
If you need connection tracking dont forget the ct state rules. Iptables vs Nftables the answer is nftables at least in the long run. Then prepare the iptables rules you wish to use by editing etcsysconfigiptables and etcsysconfigipt6tables.
Important To avoid that the different firewall services influence each other run only one of them on a RHEL host and disable the other services. Rootrhel-7 iptables -V iptables v1421 You can also identify iptables-nft by checking whether the iptables binary is a symbolic link to xtables-nft-multi. Adding a counter to an existing rule.
Of course you can enable the systemd service and have your rules restored on reboot. In this brief tutorial let us see how to replace firewall-cmd using Iptables in. Rootrhel-8 ls -al usrsbiniptables lrwxrwxrwx.
Some distributions RHEL-8 included ship predefined nftables configuration in etcnftables. The EPEL repository can be added to your system with the following command. Sudo yum install snapd.
I have a RHEL 7 IP 19216801024 and RHEL 8 IP 19216801124 host both of which are getting duplicated packets from a router which are intended for a different host IP 19216811024. Unfortunately firewallds nftables backend is unlikely to find its way to Red Hat Enterprise Linux 7.
This explains also the first two letters from this new traffic filtering solution. The bcc-tools package as a technology preview that should also enable installing bpftrace. Both iptables and nftables use the netfilter components in the Linux kernel.
Use the nftables utility to set up complex and performance critical firewalls such as for a whole network. Each rule within an IP table consists of a number of classifiers iptables matches and one connected action iptables target. Sudo systemctl enable iptables sudo systemctl start iptables.
RHEL 76 brings also support for eBPF tracing with eg. How can I use iptables on the RHEL 7 host and nftables on the RHEL 8 host to modify the destination IP so that each host receives the packet as if it was. Snap can now be installed as follows.
Sudo yum install epel-release. This will also load the kernel modules. Now install iptables service using yum package manager using the following command.
The service reads rules from etcsysconfignftablesconf. Iptables is replaced with firewall-cmd. Nftables has several advantages for me the most important are.
Firstly ensure the iptables-services package is installed. Nftables is the successor of iptables it allows for much more flexible scalable and performance packet classification. The good news is since Fedora is RHELs upstream it is likely that the nftables backend will eventually make it into some future RHEL release.
Install Iptables on CentOSRHEL 7. Systemctl disable firewalld rm etcsystemdsystembasictargetwantsfirewalld. SUSE 15 and newer.
But there are still some peoples use and familiar with traditional Iptables. There are a lot of user interfaces available to manage iptables or nftables. This increases the value of things and decreases the chance of inauthentic or pirated work appearing on different platforms.
Nftables ユーティリティーを使用してネットワーク全体など複雑なパフォーマンスに関する重要なファイアウォールを設定します iptables です. The unified rule for IPv4 and IPv6. This certifies their authenticity and creates a sense of scarcity.
Nftables를 사용하여 연결 수 제한. CentOS 7 and newer. Yum install -y -q iptables-services.
Once installed the systemd unit that. Nftables를 사용하여 연결 양 제한. Blocking IP addresses that attempt more than ten new incoming TCP connections within one minute.
The nftables scripting environment enables administrators to include other scripts by using the include statement. One of the flaws in iptables is the slightly cryptic way of expressing which information flows are allowed. Although this can be managed by firewalld experienced Linux administrators may prefer to use the native nft command.
Now check the iptables service status using below command. Download nftables-08-14el7x86_64rpm for CentOS 7 from CentOS repository. They also offer a range of digital currency which makes their platform one of the largest NFT marketplaces.
Limiting the number of connections using nftables. The low platform fees are also an excellent opportunity to make more money. The Non-fungible token or NFT acts as a certificate you attach to digital goods.
Systemctl enable nftables nft list ruleset etcsysconfignftablesconf. After installing enable iptables service and start using below commands. Most Frequently Asked Questions Rhel 7 Nftables What is an NFT.
OpenSUSE 15 and newer. RHEL 7 and newer.
Rules which are independent of IP protocol such as allow traffic on TCP port 22 can be written in such a way that a single rule applies to both protocols. Snap connect nftables-pknetwork-control Remember to update your nftables scripts to point to snapbinnft and move your scripts from etcnftables to varsnapnftables-pkcommon. Snap is available for CentOS 76 and Red Hat Enterprise Linux 76 from the Extra Packages for Enterprise Linux EPEL repository.
Each of them has the option of converting them into ETH which is the most common cryptocurrency used in OpenSea. It is the default for. The Iptables feature is not included in Centos7 and RHEL 7 by default.
Since this snap is fully confined configuration files must be placed in varsnapnftables-pkcommon.

Red Hat S Centos 8 Arrives Here S What You Get With It Fedora Unity
Installing Redhat Enterprise Linux 8 0 With Screenshots

Red Hat My Distro Review
Rhel 5 6 7 8 Cheatsheet 8 5x11 0519 0 Pdf Operating System Families Unix


Learn How To Switch From Firewalld Iptables To Nftables On Rhel Centos 7 R Sysadmin

Red Hat Enterprise Linux Rhel 8 Installation Step By Step Sevenmentor
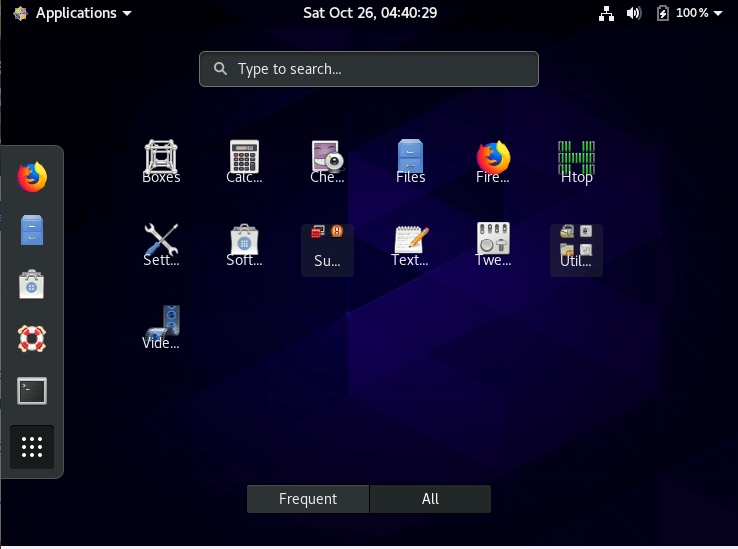
Centos 8 Release A Glance At The New Features Tutorials And How To Cloudcone

Pin By Suresh Babu Mara On Redhat Network Bridge Networking Linux
Simplylinuxfaq Rhel 8 V S 7 Differences


Red Hat Linux System Administration Sa3 Red Hat Enterprise Linux System Administrator Red Hats
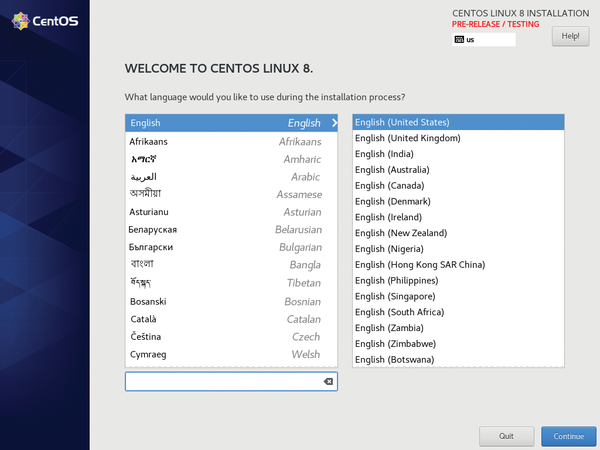
On The Dvd Admin Magazine

Using Nftables In Centos 8 And Getting Your Ready For The Rhcsa

How To Stop Start Firewall On Rhel 8 Centos 8 Linux Tutorials Learn Linux Configuration

The End Of The Centos Era Support According To The Official Information Emanating From The Redhat Company In December 2020 We Are Talking About The Termination Of Development And Support Of Centos

No comments:
Post a Comment